Supermarket Fridges Hacked, Plus 3 Tech Stories
A supermarket refrigeration cyberattack in France turned an internet-connected maintenance feature into spoiled food, fire risk, and millions of euros in losses. That is the lead today because it makes a point that can get lost in security reporting: when software controls physical equipment, a bad password, exposed controller, or missed firmware update can become an operating loss before anyone starts talking about stolen data.
Hackers changed the temperature, not just the data
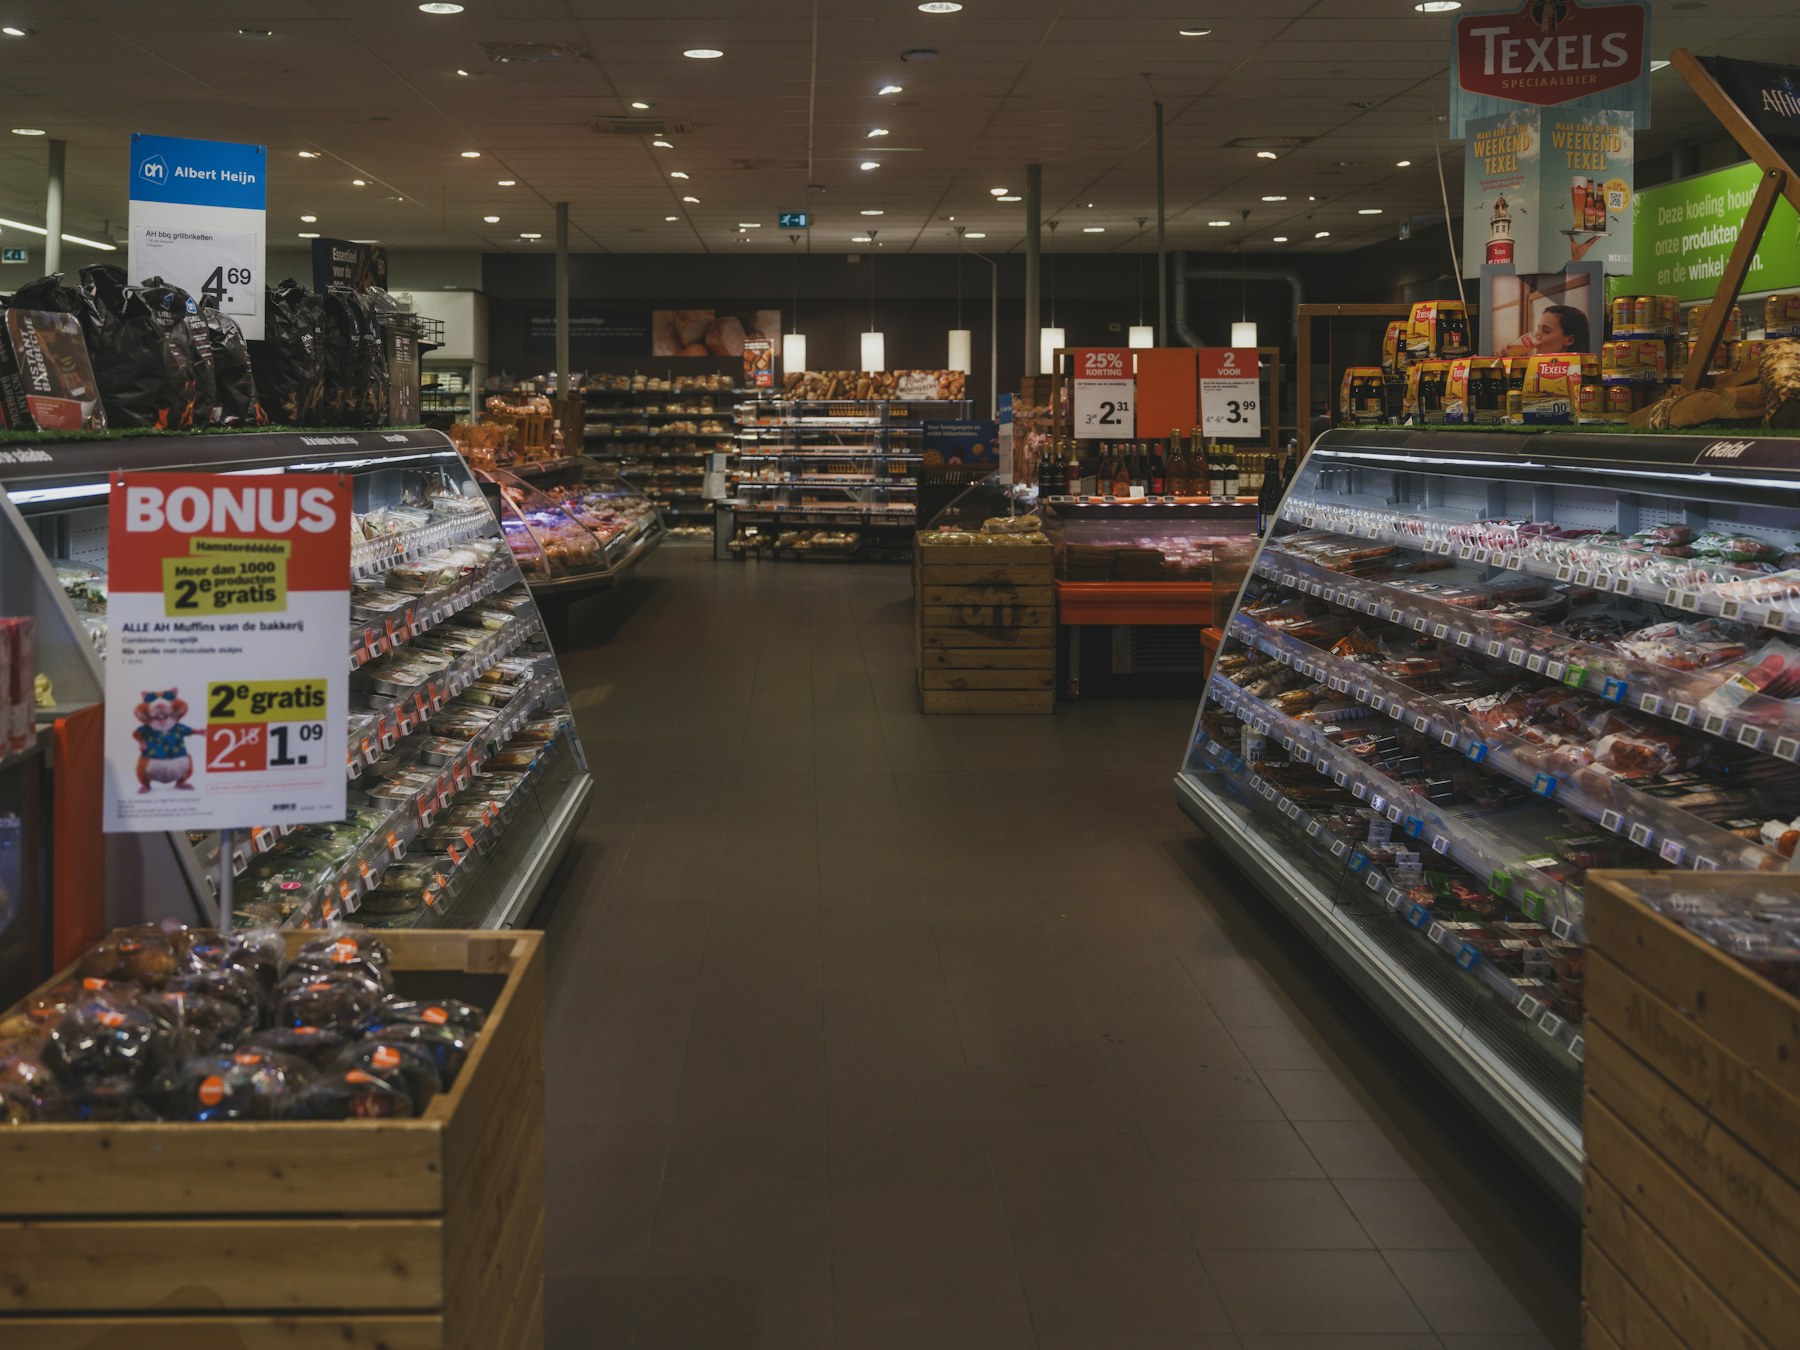
Attackers remotely raised refrigerator and freezer temperatures at hundreds of French supermarkets overnight Sunday into Monday. Carrefour said 80 stores were hit. Intermarché said about 150 stores saw equipment heated to 50°C for six hours, forcing the chain to discard the affected food. Monoprix and Coopérative U also reported impacts. France’s national cybersecurity agency, ANSSI, and the Paris prosecutor’s office are investigating.
The equipment matters here. Store refrigeration is often managed by a central controller that maintenance companies can reach over the internet. That remote access is useful when a technician needs to adjust dozens of cases without driving to the store. It is also a path into a physical process. Reuters reported that French officials identified vulnerable Danfoss software, while Danfoss said affected units were running outdated firmware. Earlier research on the Danfoss AK-SM 800A documented flaws that could let an attacker bypass authentication and run code on a controller.
The lesson isn’t that every connected freezer is waiting to catch fire. Investigators have not publicly established the attackers, the exact entry path at every store, or whether other incidents in Europe are related. The useful lesson is narrower: organizations need to know which systems can change the physical world, who can reach them remotely, and what happens when the network connection is lost or abused.
If your business depends on refrigeration, access control, cameras, HVAC, or other connected equipment, inventory the controllers as seriously as the laptops. Confirm that the firmware is supported, restrict remote access, separate these systems from ordinary office traffic, and test the manual fallback. A backup of the office server won’t save a freezer full of food. Recovery has to include the equipment and the operating procedure.
Business IT goes well beyond the website
Your business also depends on workstations, cloud accounts, browsers, Wi-Fi, remote access, collaboration tools, and all the other technology that quietly becomes infrastructure. Raymond Tec works across that whole stack, whether the problem lives on a server, on a desk, or somewhere in between.
Bricksforge sites need an update and a closer look
WordPress owners using the commercial Bricksforge add-on should update now. Security researchers say attackers are actively exploiting CVE-2026-85097 in Bricksforge 3.1.8.9 and earlier. The fixed 3.x release is 3.1.8.10, and the vendor’s current 4.x line includes the hardening as well.
This one is more than a scary score. The plugin checks an uploaded file’s MIME type, but the vulnerable form workflow trusted separate, attacker-controlled metadata about where that file should go. An attacker could submit a file that passed the image check as a GIF and then make the destination end in .php. The web server would treat it as executable code. No WordPress login was required.
Patchstack says it first observed exploitation attempts on October 7. Updating closes the hole, but it does not remove code that may already have been planted. If an exposed site ran a vulnerable version, inspect logs for requests to the Bricksforge form endpoint, look for unexpected PHP files under uploads, review administrator accounts, and check for unexplained changes. If you find indicators, treat it as a compromise, not a routine plugin update.
This is also a reminder to include paid plugins in the same inventory as WordPress core. A license lapse can quietly become a security problem when it also stops updates. The important question isn’t only “Do we have backups?” It is “Can the same account or compromised site erase those backups too?” Keep a recoverable copy outside the live hosting account.
WordPress security & maintenance
Keeping WordPress current is only part of keeping it healthy. Raymond Tec handles updates, backups, security monitoring, compatibility problems, access cleanup, and maintenance — plus the assorted weirdness that accumulates on a site over time.
Your workplace chat may be someone else’s training set
Business Insider reports that data brokers and AI-training startups are offering some companies six-figure deals for workplace material, including Slack messages, email, internal documents, and recordings. The pitch is that the material can be anonymized and sold to model developers hungry for realistic examples of how people communicate and complete work.
“Anonymized” is doing a lot of work in that sentence. Removing names does not automatically remove customer details, trade secrets, health information, personnel discussions, writing patterns, project histories, or enough context to identify people again. Direct messages can also feel private to employees even when company policy says the employer controls the workspace. Legal ownership and reasonable expectation are not always the same thing.
For a small business, a data deal might look like found money. I would treat it as a decision about employees, customers, contracts, and future control, not a new revenue line to approve from an inbox. Before sharing anything, determine exactly which channels and files are included, whether employees and customers consented, how the buyer prevents re-identification, which subcontractors receive copies, how deletion works, and whether your existing agreements allow the transfer. If the answers are vague, the dataset is not ready to leave the building.
Turning on AI is the easy part
Deciding what an AI tool should be allowed to see, who should use it, what work it should perform, and what happens when it gets something wrong is the more interesting problem. Raymond Tec helps businesses connect and automate the tools they actually use without treating every new feature like a button that obviously needs to be switched on.
Regulators are asking banks who can stop the AI agent
U.S. and European banking regulators are asking banks how they control more autonomous AI systems, according to Reuters. The questions include who is accountable for an agent’s decisions, whether staff can shut it down, how an institution detects malicious behavior, and how it restores operations after a cyberattack. Regulators are gathering information; this is not a new rule or an order for consumers to change anything today.
Still, the questions are worth borrowing outside banking. As I explained in AI Agents Need Boundaries They Can’t Rewrite, an AI agent that can read files, send messages, move customer records, approve work, or trigger payments is not merely a chatbot with better manners. It is a software identity with permissions. Give it only the systems and data required for the job, require human approval for irreversible steps, log what it does, and make sure someone can revoke its access without asking the agent for permission.
I think the recovery question is the best one. Prevention gets the polished demos, but businesses live with the aftermath. If an agent changes thousands of records or a compromised controller ruins inventory, can you tell what changed, restore a known-good state, and keep serving customers while you investigate? That is where useful technology ends and operational wishful thinking begins.
Technology has an annoying habit of connecting to everything else. Browse the News archive for current stories, or dig into Raymond Tec Insights for longer pieces about what building, fixing, maintaining, and living with this stuff actually looks like.
Sources / Further Reading
- Reuters: Hackers heat French supermarket fridges, sparking fires and spoiling food
- Le Monde: A disastrous day for French supermarkets after the refrigeration attack
- Claroty Team82: Danfoss AK-SM 800A vulnerability research
- Patchstack: Bricksforge vulnerability and exploitation details
- NVD: CVE-2026-85097
- Bricksforge version changelog
- Business Insider: The market for workplace data used in AI training
- Reuters: Banking watchdogs increase scrutiny of agentic AI controls
- Photo by Haberdoedas on Unsplash.